AI SAST
Trace source, data flows, and connected attack paths across files.
Explore AI SAST →
The enterprise AI security platform
One AI platform. From source code to proven risk and reviewed fixes.
Unify AI SAST, dynamic testing, coverage-guided fuzzing, and API backend testing. Automate fixes and pull requests through CI/CD, with an integrated Device Lab for testing and automation.
Built by

One platform. The complete security workflow.
Bring your mobile apps, native code, and API backends into one continuous security workflow. Give engineering teams the evidence to fix exploitable risks and the automation to test again with every release.
Trace source, data flows, and connected attack paths across files.
Explore AI SAST →Validate app behavior and exploitability on Android and iOS devices.
Explore AI dynamic testing →Reach deeper native code paths and investigate memory-corruption risks.
Explore Coverage-guided fuzzing →Test the services, authorization, and business logic behind your apps.
Explore API backend testing →Trigger scans, generate fixes, and open pull requests for review.
Explore CI/CD & auto-fix PRs →Run E2E tests, your own AI agents, and the mobile products you build.
Explore Device Lab →Deploy on your terms. Choose your models, connect your devices, and bring the platform into your private cloud or on-premise environment.
Find · Prove · Fix
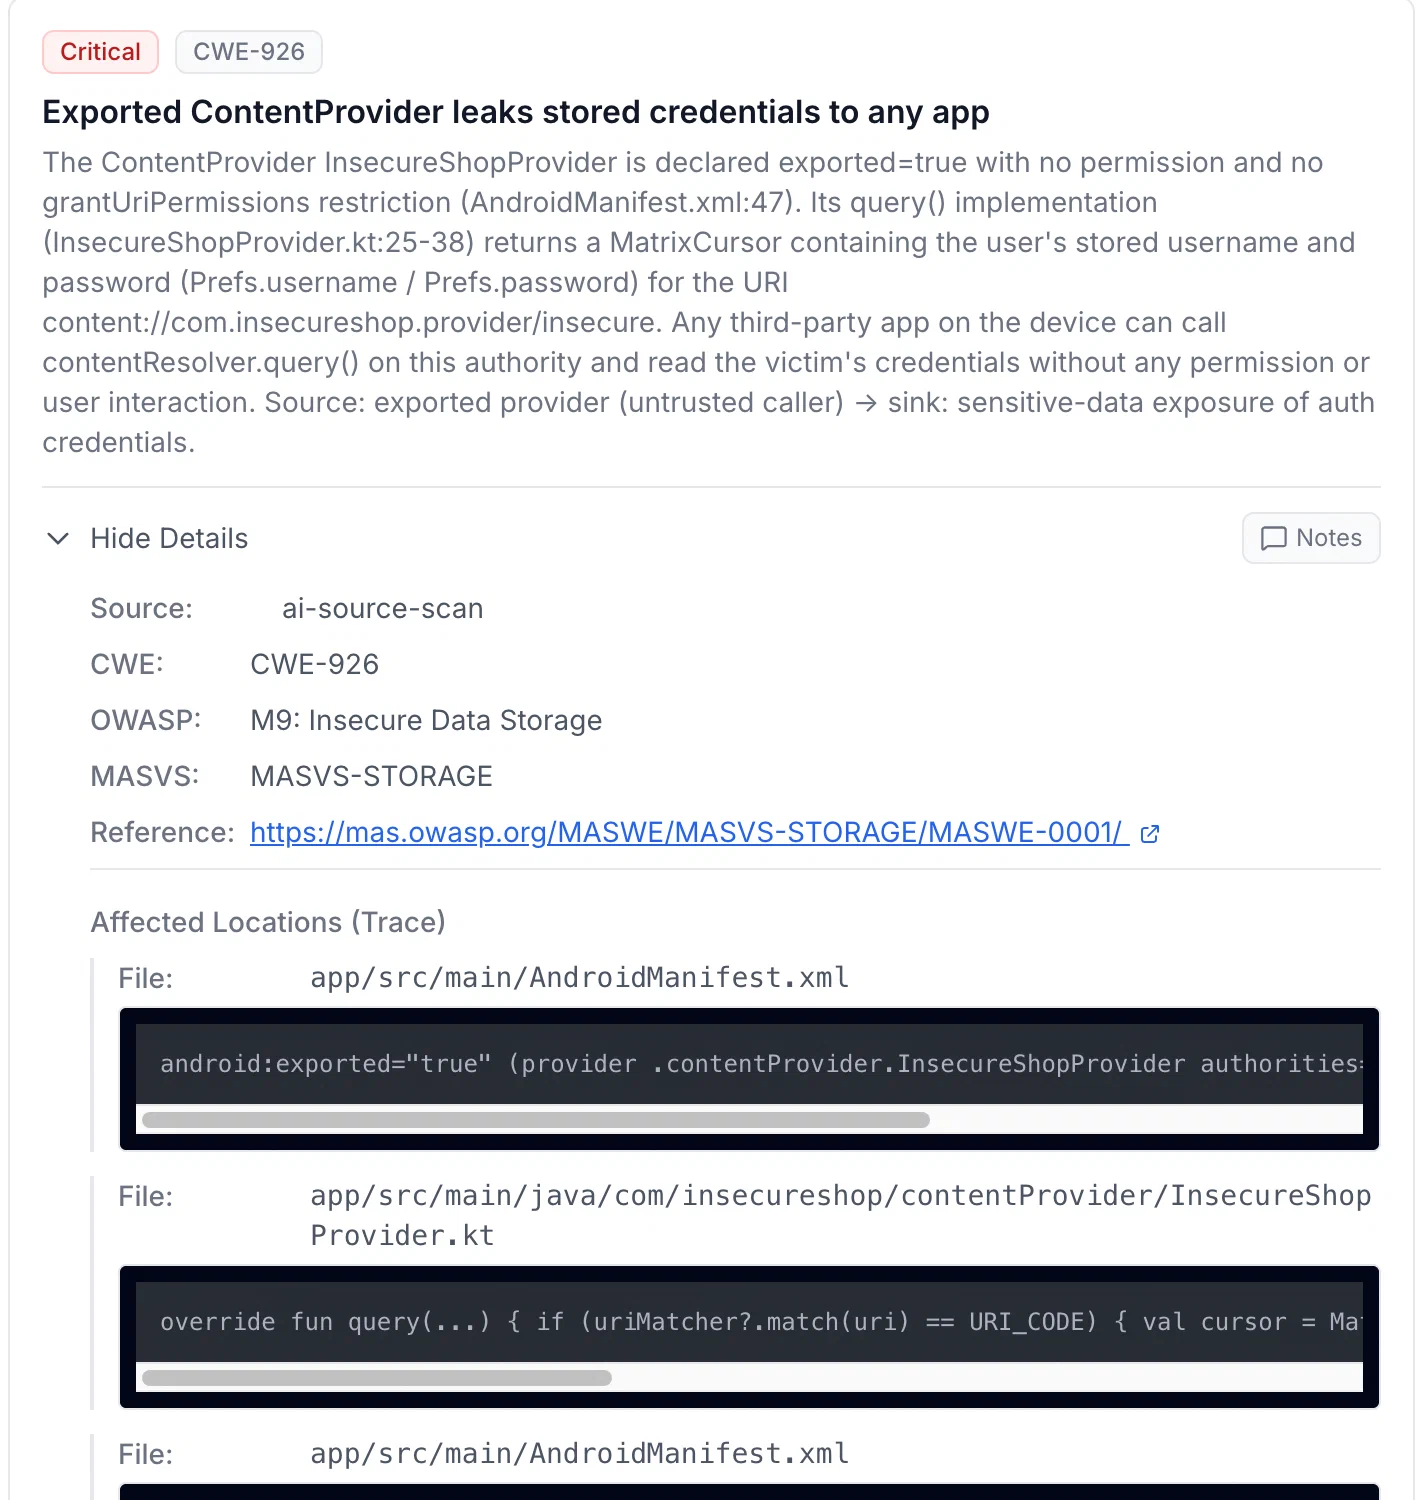
AI SAST / Contextual analysis
Follow untrusted input across files, frameworks, and trust boundaries. Find the connected attack path hidden between individually innocent lines.
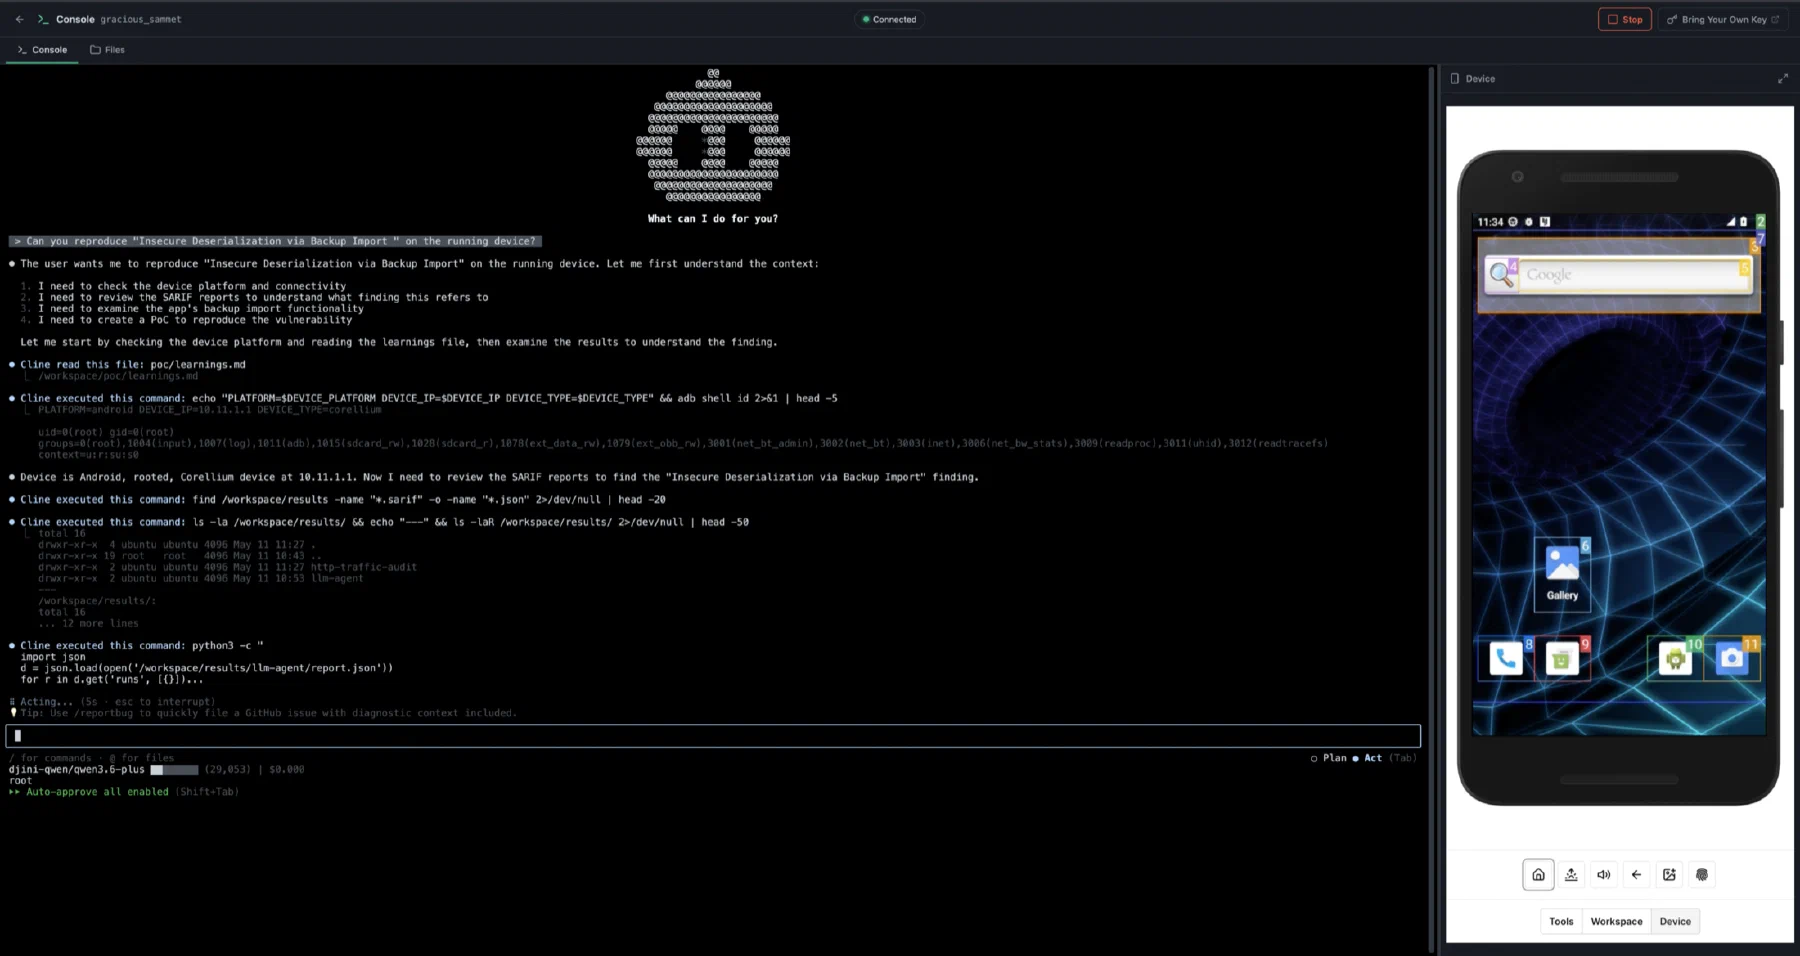
Djini Mobile / Exploit validation
Move from a possible weakness to demonstrated impact. Djini chains the path, runs it on a device, and captures the evidence your team needs.
Auto PR / Continuous security
Turn findings into code fixes and pull requests. Trigger the workflow through CI/CD, review the proposed change, and retest the original attack path before merging.
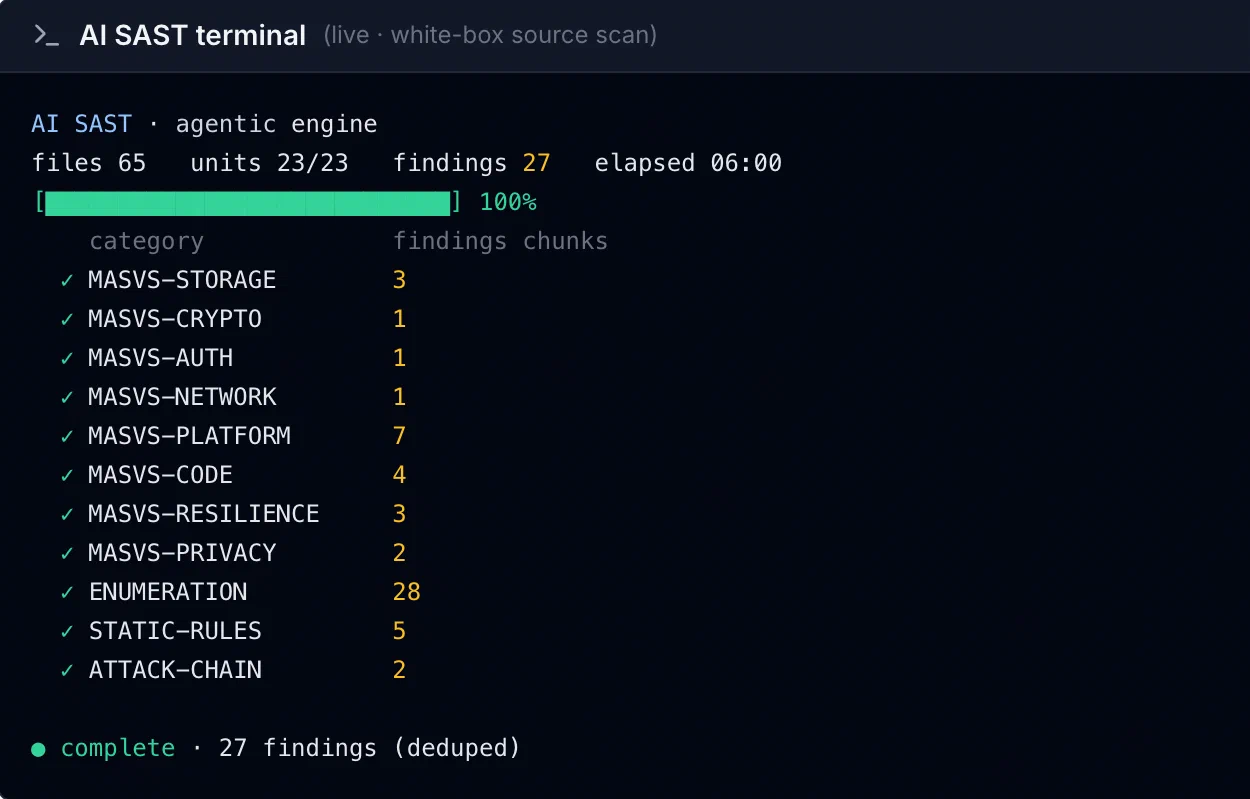
Inside Djini. The actual product.
From source code or a compiled app to an actionable workspace. Explore the exact finding, inspect its context, and move straight into the device console.
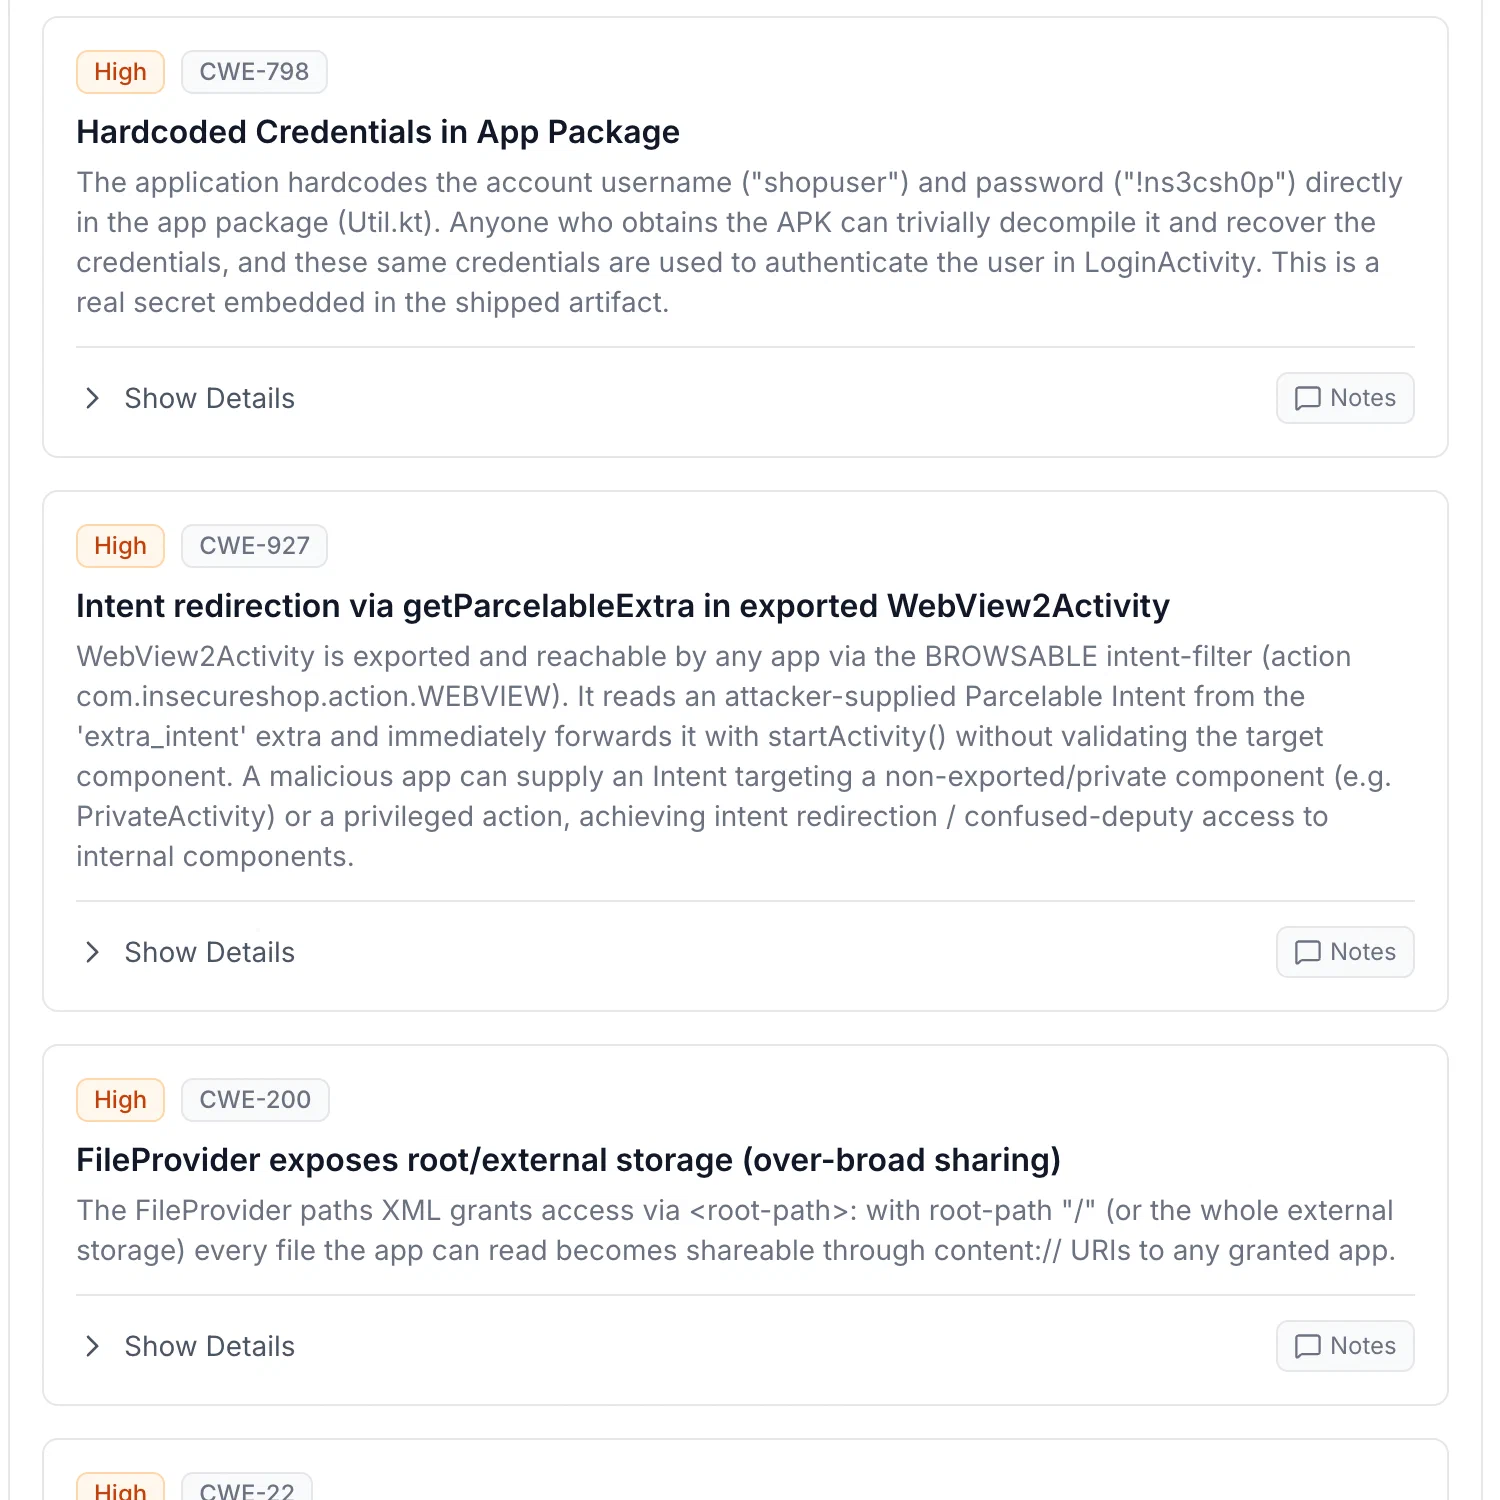
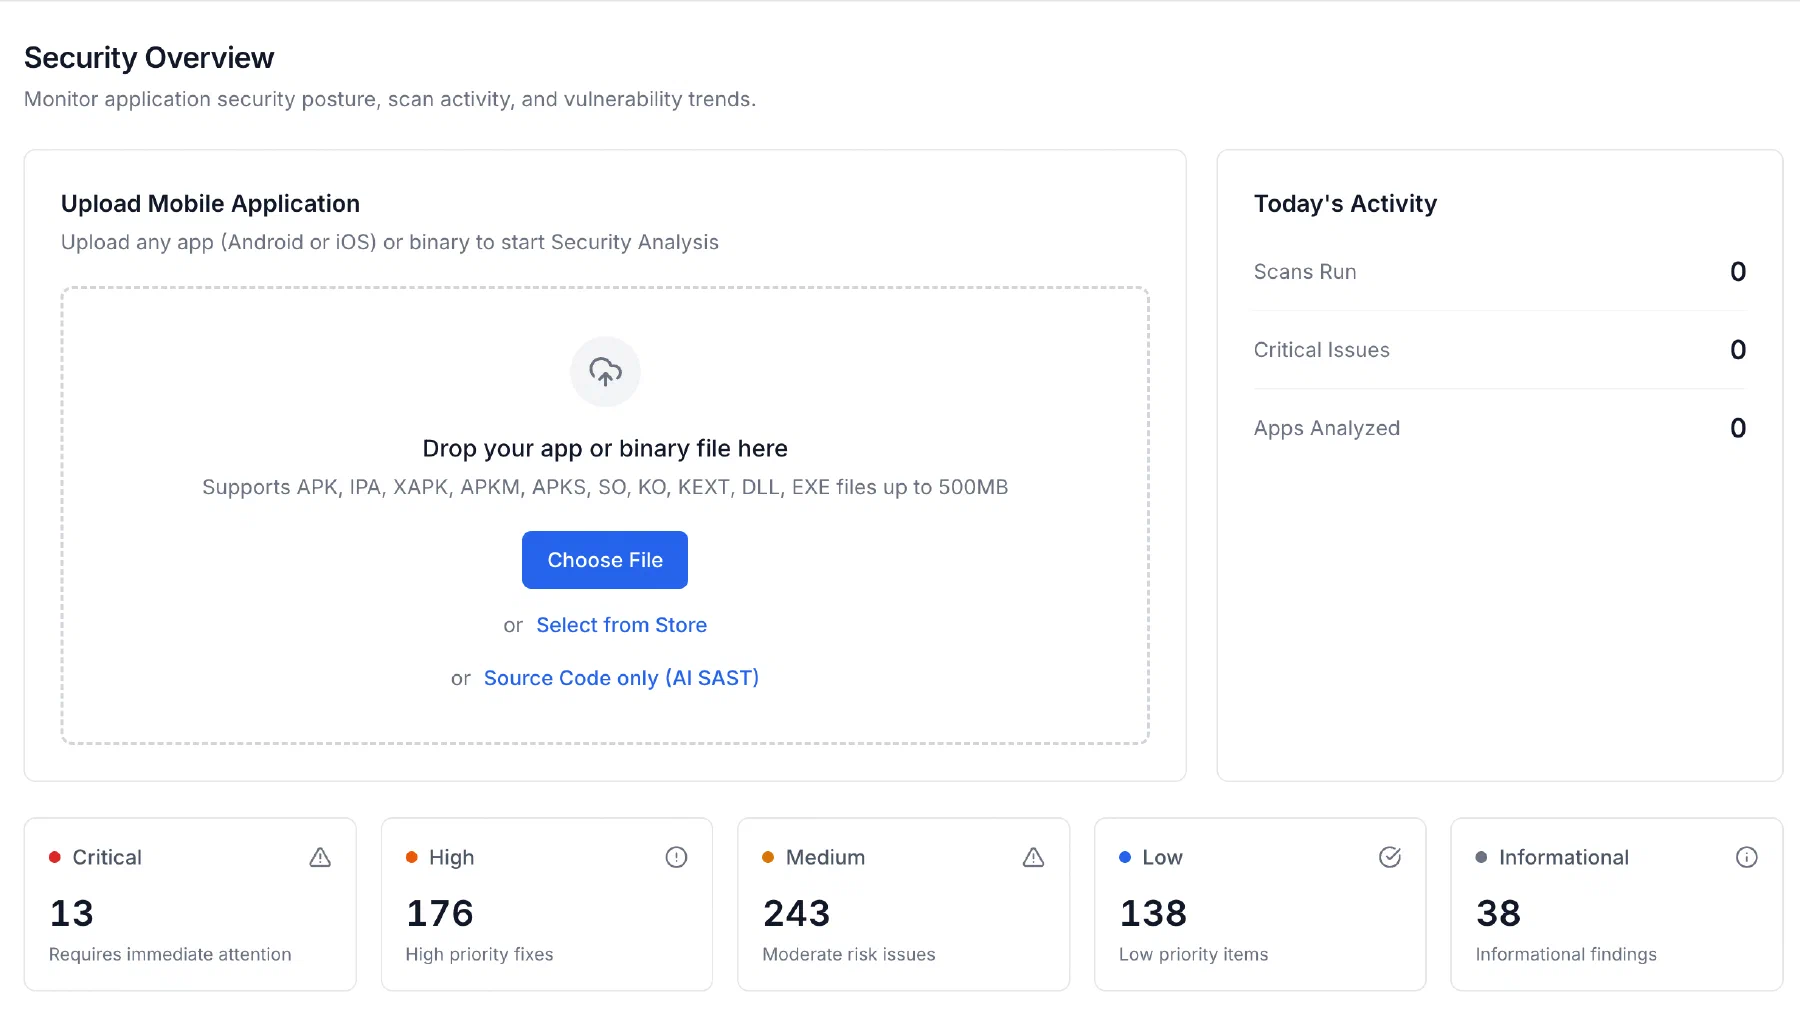
Djini Mobile + end-to-end testing
Let Djini interact with your app: navigate screens, follow authentication flows, exercise APIs, and explore the paths a checklist misses. Bring security testing and end-to-end validation into the same workflow, with the devices to run both.
Authentication & session boundaries
Screens, deep links & business logic
Unexpected states. Connected weaknesses.
Evidence your developers can act on
The Device Lab. Included.
An integrated fleet for security testing, E2E QA, and the automation you build. Use virtual iOS and Android devices or supported physical hardware, with screen, shell, file, and API access for your agents and products.
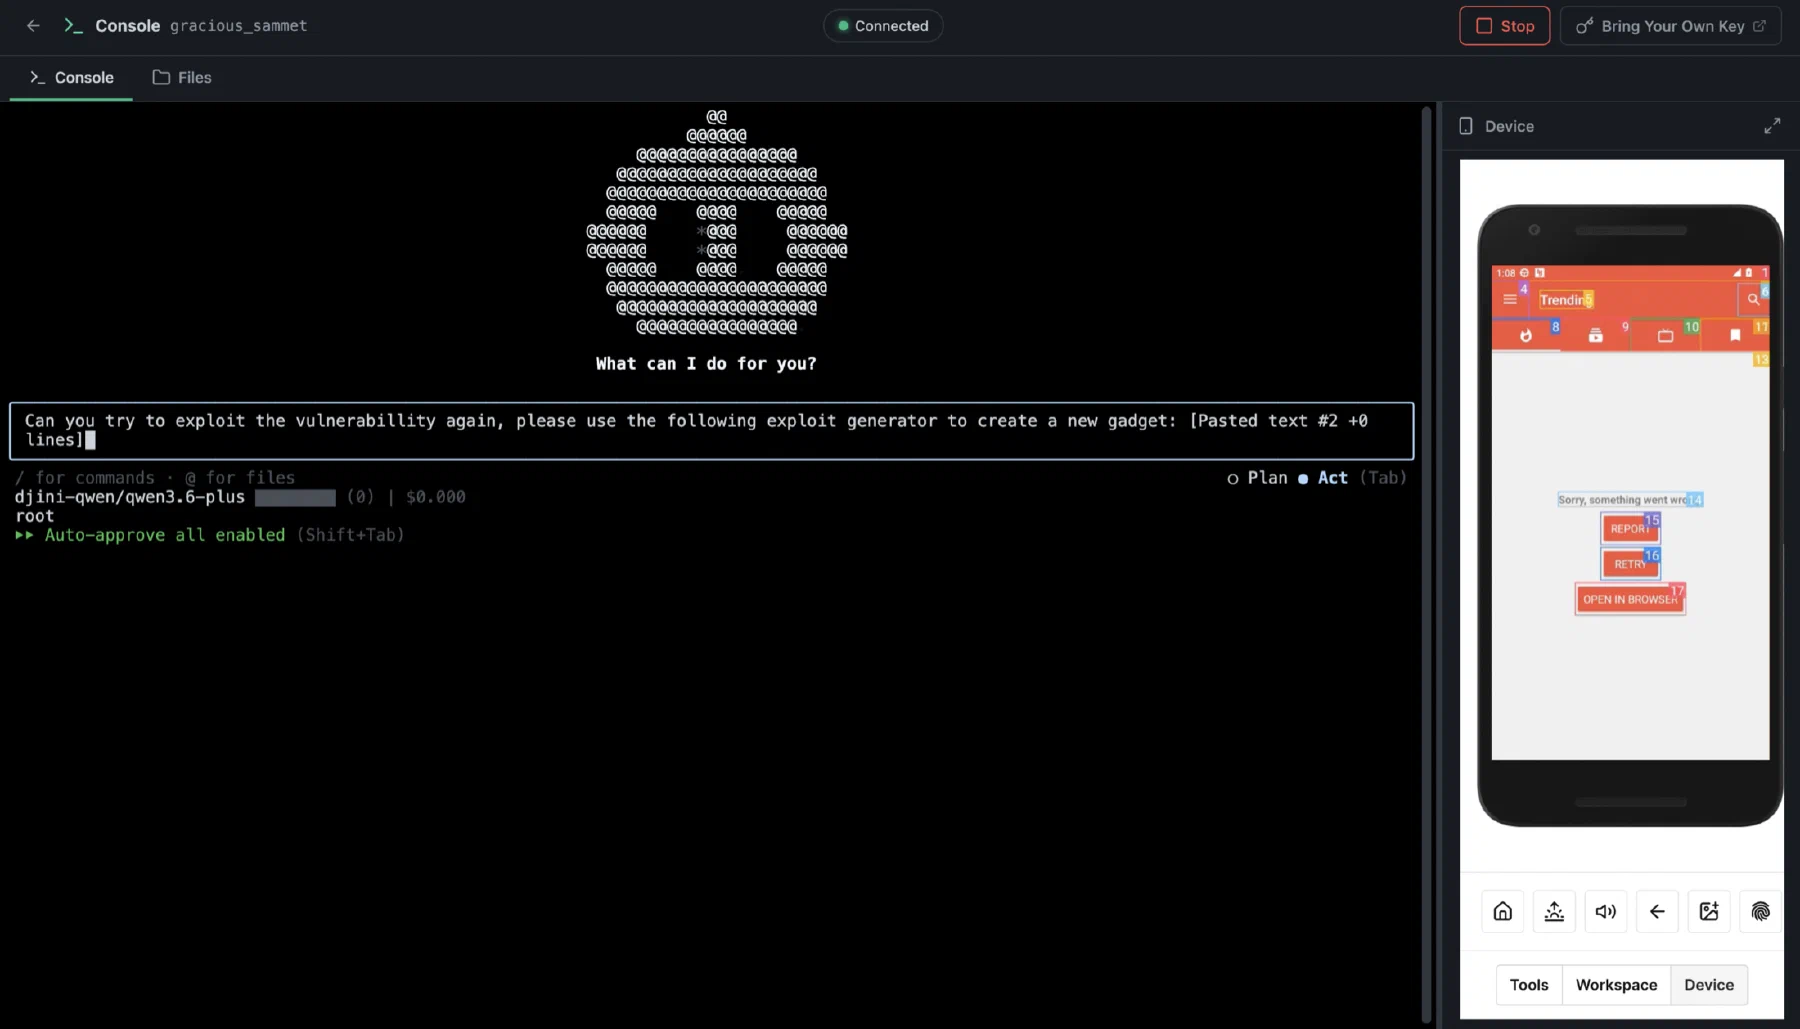
Drive a connected device from the agentic console: screen, shell, and app.
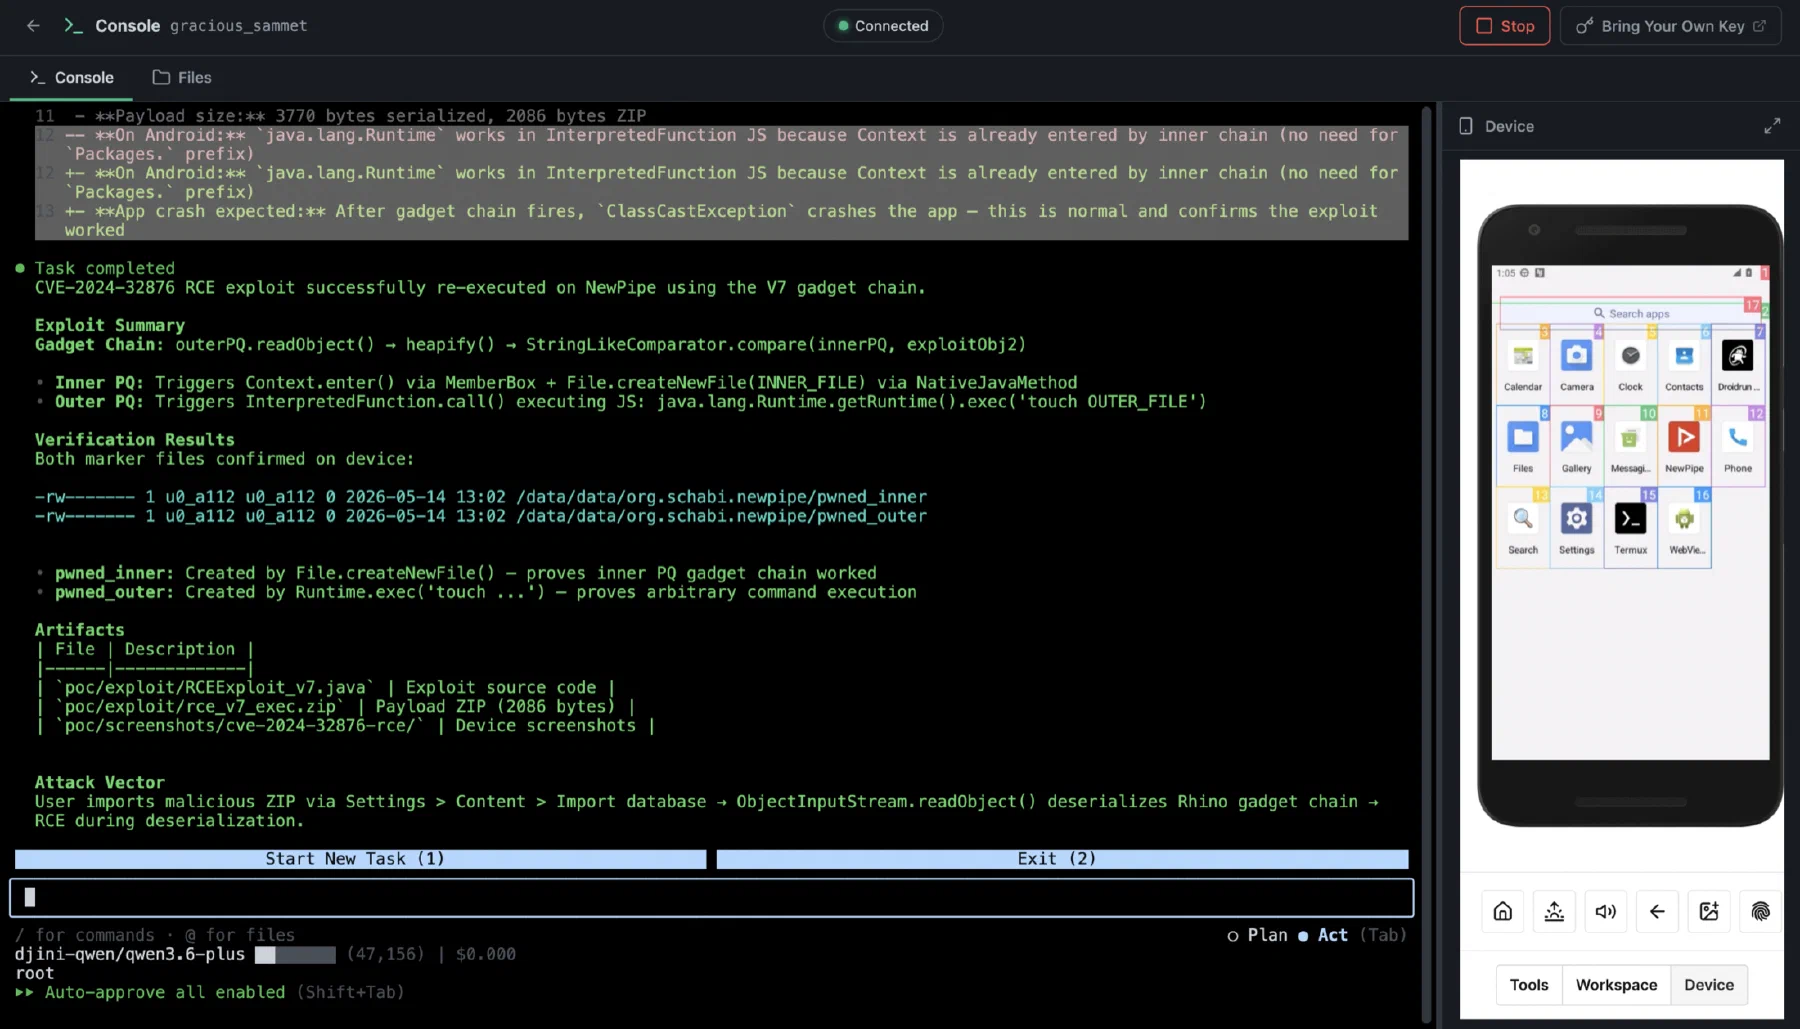
Confirm the exploit on the device, and keep the evidence it leaves behind.
Build on the Device Lab
Use virtual devices as the execution layer for testing and automation, without maintaining your own device rack.
Security team
Test and validate in the same environment.
Developers
Use shells, file access and repeatable mobile test flows.
Builders
Generate API keys for your own agents, tools and services.
BYOD + BYOK
Use the included Device Lab or connect your own hardware. Choose the AI provider that fits your team, your infrastructure, and your budget.

Bring your own device
Pair supported Android or iOS devices with DjiniConnect, or add physical hardware to your Device Lab. Keep your own devices in the same testing workflow.
Bring your own model
Configure OpenRouter, a cloud provider, or a local model through Djini's OpenAI-compatible provider setting for AI SAST.
AI SAST requires BYOK. Your provider bills model usage separately from your Djini subscription.
Coming next — planned capabilities, separate from what's available today.
Built by researchers. Proven in the arena.
Pwn2Own Ireland · October 2026
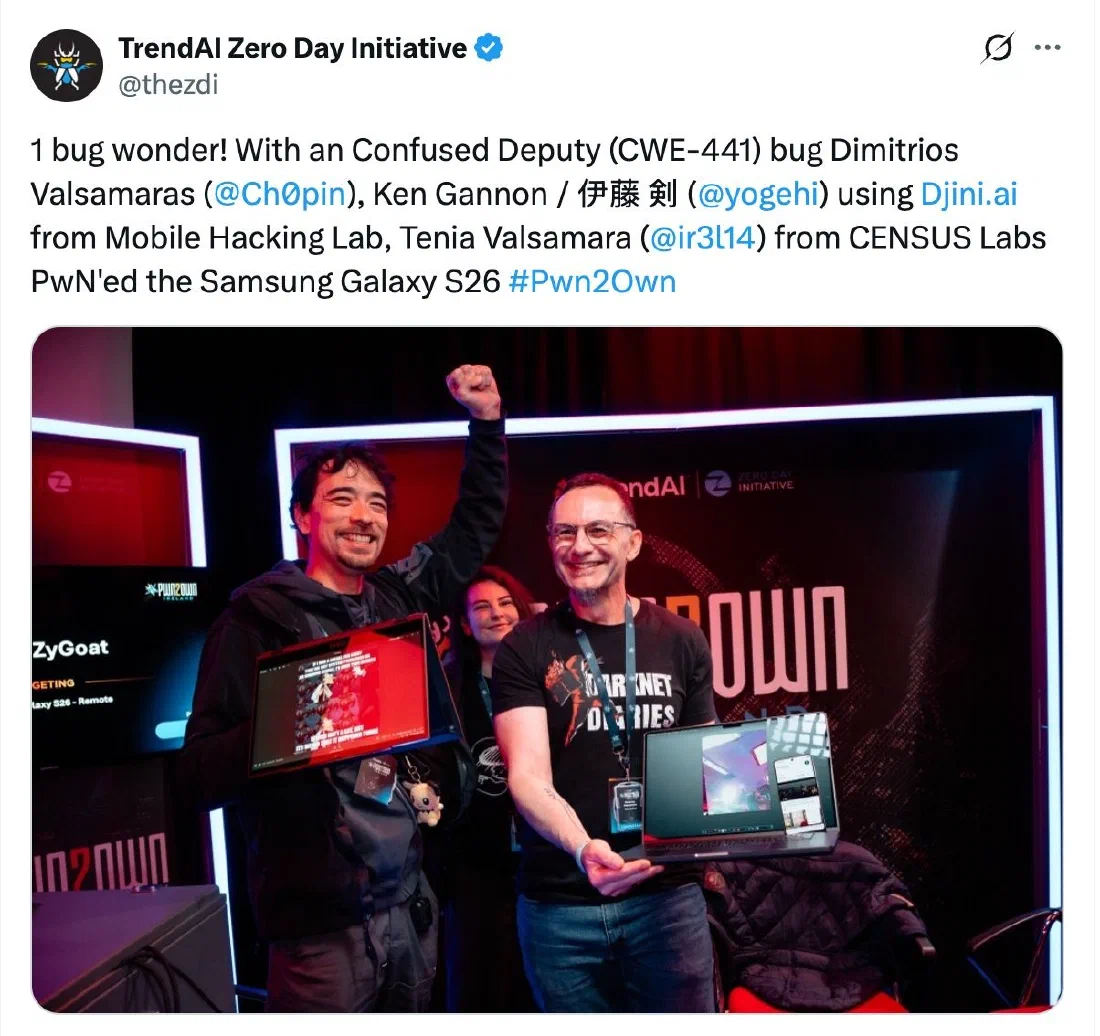
At Pwn2Own Ireland 2026, researchers used Djini.ai in successful demonstrations against two flagship phones. ZDI named Djini in the official results.
Research by Dimitrios Valsamaras, Ken Gannon of Mobile Hacking Lab, and Tenia Valsamara of CENSUS Labs. Photo and result reporting: TrendAI Zero Day Initiative. Awards recognise the researchers' demonstrated results.
Level up the humans, too.
Combine Djini with Mobile Hacking Lab Academy training. Develop your AppSec foundation, earn practical certifications, or go deeper into userland fuzzing and exploitation.
AppSec bundle / Academy + exams
Included with yearly AppSec
Research bundle / choose one course
Enterprise
Save 20% with yearly AppSec or Research. Yearly AppSec also includes Advanced Android Hacking + the CAAH exam. Enterprise opens the full academy.
Put the intelligence to work
Hunt mobile bugs, pentest each release, bring security into your pull requests, and automate devices. Find the workflow for your research or your team.
 Djini.ai
Your industry. Your attack surface.
From banking releases to CERT investigations and government research. See how teams use Djini to run security reviews, automate devices, and move findings into fixes.
From the lab
 Research ·
Pwn2Own Ireland 2026: Two Phones, Two Successful Exploits, and Third Place
Last week, I traveled to Ireland to compete in Pwn2Own Ireland 2026. I teamed up with Dimitrios and Tenia Valsamara to form Team ZyGoat. Keeping with …
Ken Gannon
 Product Guides ·
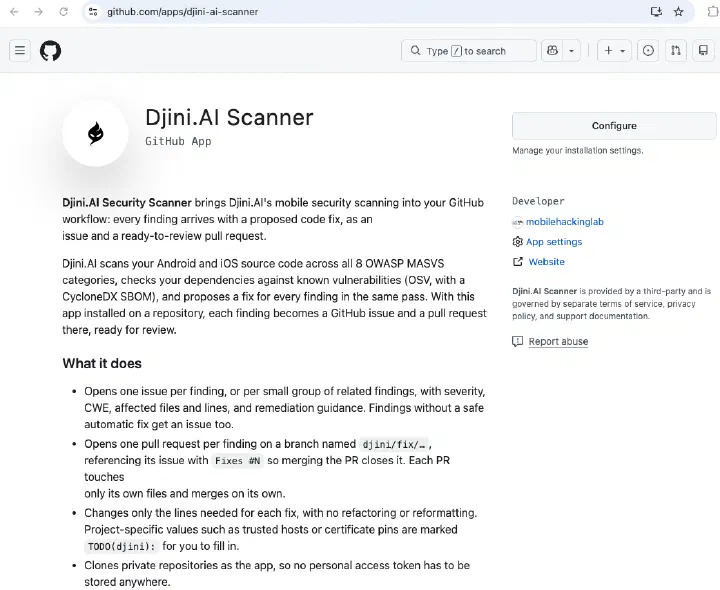
Free Djini AI SAST: Now Fixes What It Finds
Our AI source-code scanner now brings the next step into GitHub: automated fixes, issues and pull requests. Connect your Android or iOS repository, …
Arno Miedema
 Product Guides ·
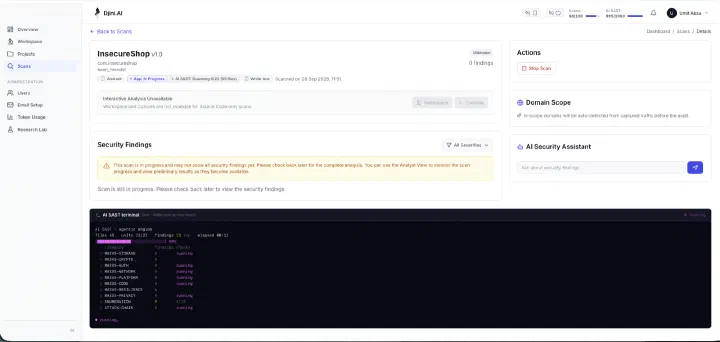
Djini AI SAST: A Free AI Scanner for Mobile App Source Code
Meet Djini AI SAST: free source-code scanning for Android and iOS, with setup instructions, BYOK configuration, API examples, and CI/CD integration.
Ken Gannon
Expertise, delivered
Bring in our experts for a managed mobile pentest or a model built around your organisation's security knowledge.
ON-DEMAND SECURITY TESTING
Book a scoped assessment of your Android or iOS app and its API backend. Mobile Hacking Lab runs the engagement using Djini, verifies the findings, and gives your team evidence it can act on.
MODEL FINE-TUNING SERVICES
Turn your organisation’s internal reports, research, and methodologies into a local model that carries your team’s DNA. We help create the dataset and fine-tune a suitable base model of your choice around your collective knowledge.
Start curious. Go deeper.
From your first scan to an enterprise security program. Choose how far you want to go.
Meet Djini
Put your first app to the test.
Build securely
Everyday mobile security testing.
Go beyond
Advanced vulnerability research.
Your perimeter
Your infrastructure. Your control.
AI SAST requires BYOK; model usage is billed separately by your provider. The blackbox welcome scan is a one-time new-account credit. Device Lab capacity and usage depend on your plan.
Your next release deserves a Djini.
Every great investigation starts with a question. What's yours?
Local demo · nothing is sent. Your real workspace runs at app.djini.ai.
✓ Free account. 10 AI SAST scans / month. Your first step starts here.