
07 / CERTS & CSIRTS

From vulnerability report to verified impact.

Give incident response and vulnerability coordination teams a connected mobile research environment. Investigate Android and iOS components, reproduce reported behavior on devices, and develop evidence for disclosure and remediation.

  1. 01
    INTAKEReport, affected build, and research question
  2. 02
    RESEARCH LABReverse engineering + focused fuzzing
  3. 03
    DEVICE LABReproduce and assess practical impact
  4. 04
    COORDINATIONAffected versions, evidence, and fix checks

ADVANCED RESEARCH / REPORT VERIFICATION / COORDINATED DISCLOSURESourceRuntimeEvidence

MOBILE SECURITY USE CASES FOR CERTS & CSIRTS

Turn a reported risk into evidence your team can stand behind.

CERTs and CSIRTs need to understand whether a report is reproducible, which versions are affected, and what a fix changes. Connect source and binary investigation with controlled device execution instead of passing disconnected notes between tools.

01 / Industry use case

Investigate beyond the initial finding

A crash or suspicious code path is a starting point. Your team needs to understand its cause, reachability, and practical security impact.

Explore the workflow →

How Djini does the work

Use Djini to investigate a mobile binary or native component, inspect decompiled code, and develop a focused fuzzing experiment. Follow promising results with device execution and a reproducible test case for researcher review.

The outcome for your team

An investigation linking the affected component, triggering conditions, crash or runtime behavior, and the evidence supporting the impact assessment.
02 / Industry use case

Verify incoming vulnerability reports

Reports from vendors, researchers, and AI-assisted tools vary in detail. Coordination teams need a repeatable way to separate demonstrated impact from claims that still need work.

Explore the workflow →

How Djini does the work

Scope an AppSec Portal workflow that brings the submitted steps and build into Device Lab. Reproduce the claim, collect observations, and return a reviewable outcome: verified, needs information, or not reproduced.

The outcome for your team

Reproduction context, device and build details, supporting artifacts, and outstanding questions that help your analysts coordinate the next step.

03 / Industry use case

Build a private mobile research lab

Unpublished findings, vendor builds, and investigation material need an environment that matches the team’s data and operational requirements.

Explore the workflow →

How Djini does the work

Plan a private Djini deployment with approved models and a controlled device fleet. Define how builds, prompts, findings, and device artifacts move through the research and fix-validation workflow.

The outcome for your team

A scoped research environment with documented processing boundaries, repeatable device experiments, and a path to validate vendor fixes.

YOUR FIRST EVALUATION

Bring a report you want to understand deeply.

Choose a reported mobile issue, the affected build, and a controlled device environment. Reproduce the behavior, investigate the root cause, then compare the original and fixed versions with the same test.

Start with the first workflow →

Research targets, device and OS support, model processing, and enterprise coordination are agreed during scoping.

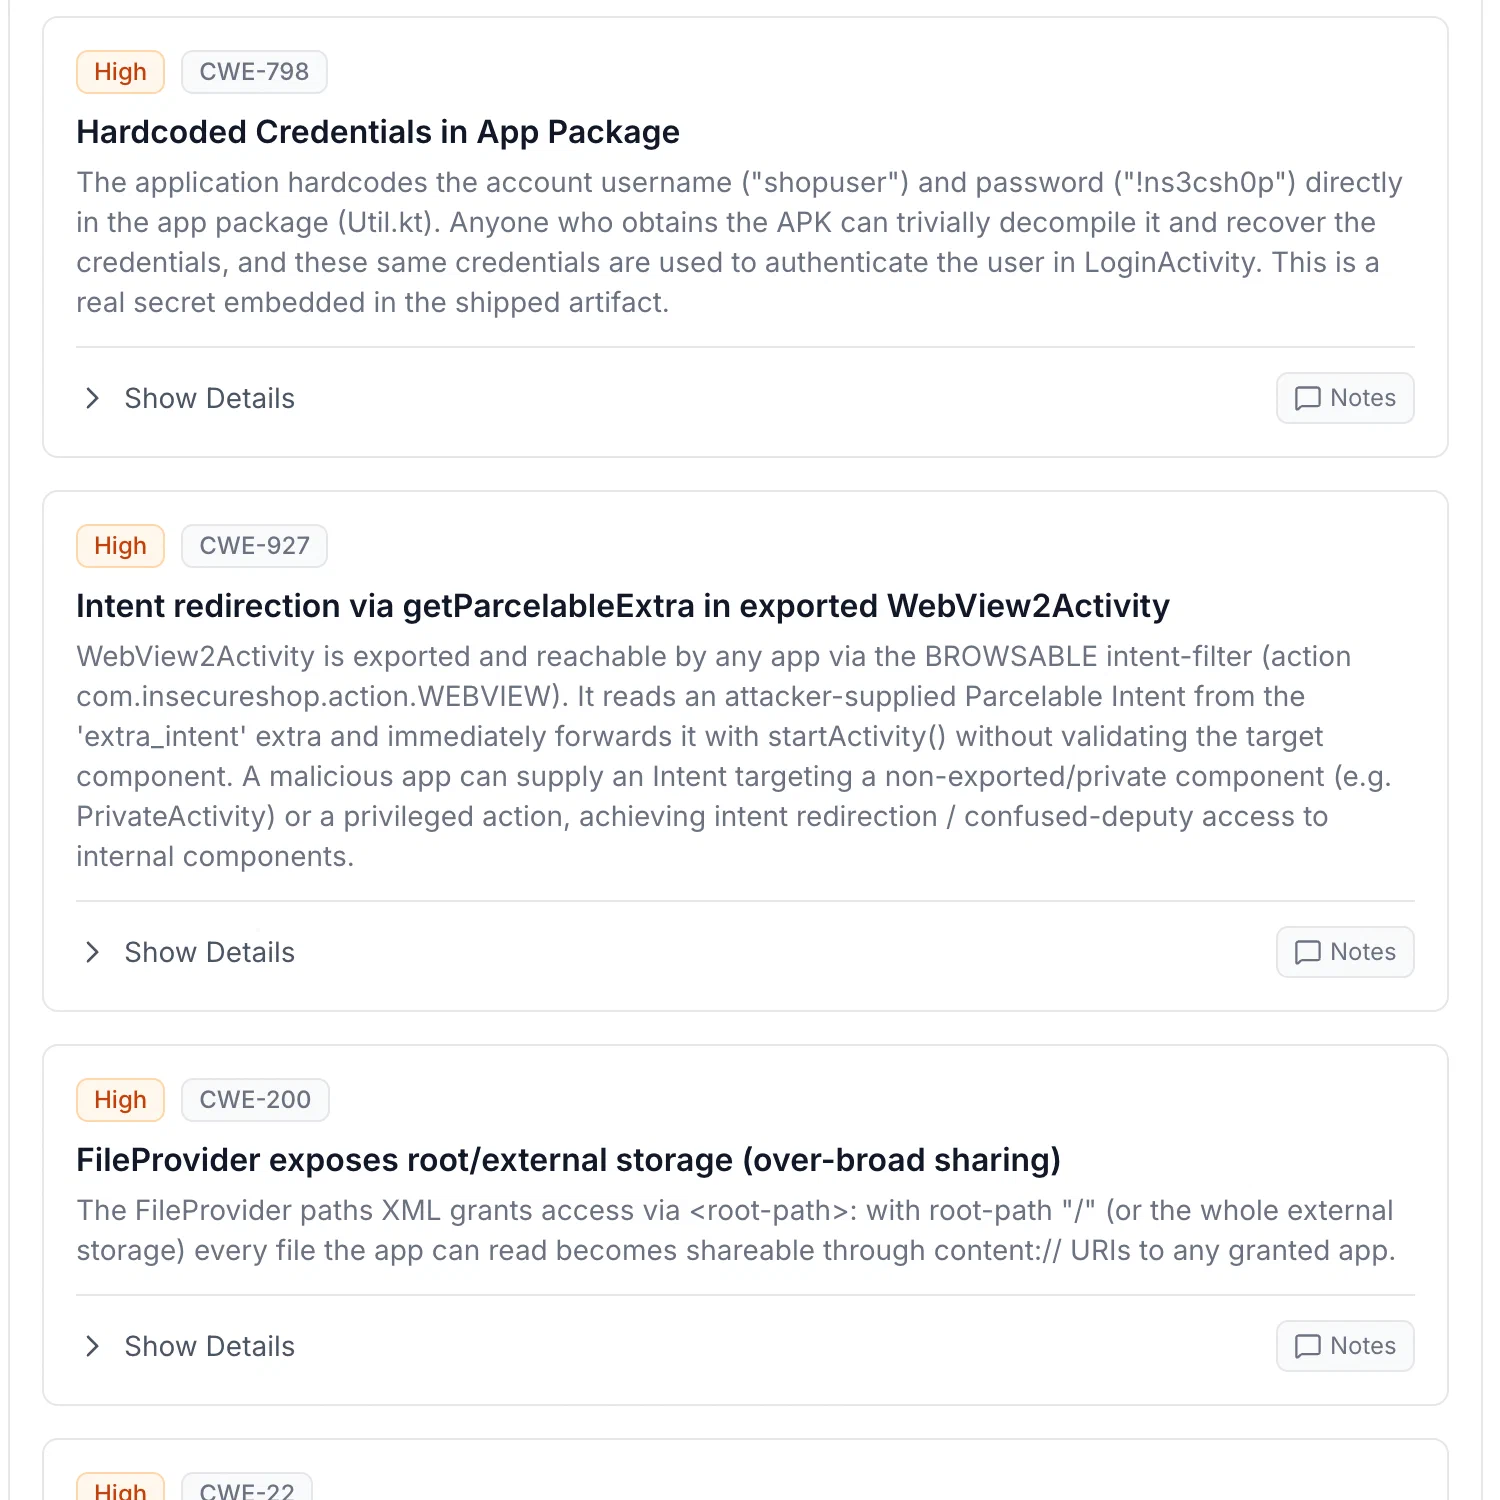
Djini AI SAST findings for the InsecureShop training app, ranked by severity with their CWE mapping

Build your workflow · All Djini use cases →

A few good questions

Before you go deeper.

Can Djini support coordinated vulnerability disclosure?

Djini can support the technical investigation, reproduction, and fix-validation work around a disclosure. Your team retains responsibility for the disclosure process, vendor communication, and advisory publication.

Does a failed reproduction mean a report is invalid?

No. Missing setup details, device differences, timing, or incomplete test coverage can prevent reproduction. Preserve the evidence and uncertainty so an analyst can request more information or continue the investigation.

Can we investigate without source code?

Black-box mobile testing and binary investigation are part of the platform’s workflows. The specific target, native research requirements, supported device environment, and enterprise integrations are scoped with the team.

DJINI FOR CERTS & CSIRTS

Your next investigation. Evidence for the next decision.

Connect the code, the device, and the question your team needs answered.