
01 / FINTECH & BANKING

Banking app security. Part of every release.

Put mobile and API pentesting into the release process. Djini operates your app, follows important banking journeys, and gives the mobile and backend teams evidence they can use to fix and retest.

  1. 01
    RELEASEBanking build + defined test accounts
  2. 02
    DJINI AIOperate the app and follow API journeys
  3. 03
    DEVICE LABValidate a connected attack path
  4. 04
    ENGINEERINGEvidence → fix workflow → retest

RELEASE TESTING / DEVELOPER FIXES / PRIVATE DEPLOYMENTSourceRuntimeEvidence

MOBILE SECURITY USE CASES FOR FINANCE

A security capability that keeps pace with delivery.

Use Djini across the work a banking team actually needs to complete: review the next release, fix risks while code is changing, and run the testing capability within an agreed enterprise boundary.

01 / Industry use case

Pentest each banking-app release

Mobile and API teams ship changes together. Security review needs to follow the complete customer journey through both.

Explore the workflow →

How Djini does the work

Give Djini a test build and account roles. Ask it to operate an agreed onboarding or payment flow, investigate the trust decisions behind the screens, and validate a suspected attack path on a device.

The outcome for your team

A reproducible investigation with the affected app/API behavior, device context, and evidence to use in remediation and retesting.
02 / Industry use case

Fix security issues before the merge

Developers need findings while they still have the code change in context, with a clear route to a reviewed fix.

Explore the workflow →

How Djini does the work

Run AI SAST from the repository or CI/CD pipeline. Feed source locations and connected attack paths to your coding agent so it can propose a focused patch and pull request.

The outcome for your team

Code findings with remediation context and a proposed change for your normal repository review and rescan workflow.

YOUR FIRST EVALUATION

Start with a release your team knows well.

Choose one app build and one important customer journey. Compare Djini’s investigation with the behavior your team expects, then use the same reproduction path to check a fix.

Start with the first workflow →

Start with an agreed app build, test accounts, and scope. Device usage depends on your plan.

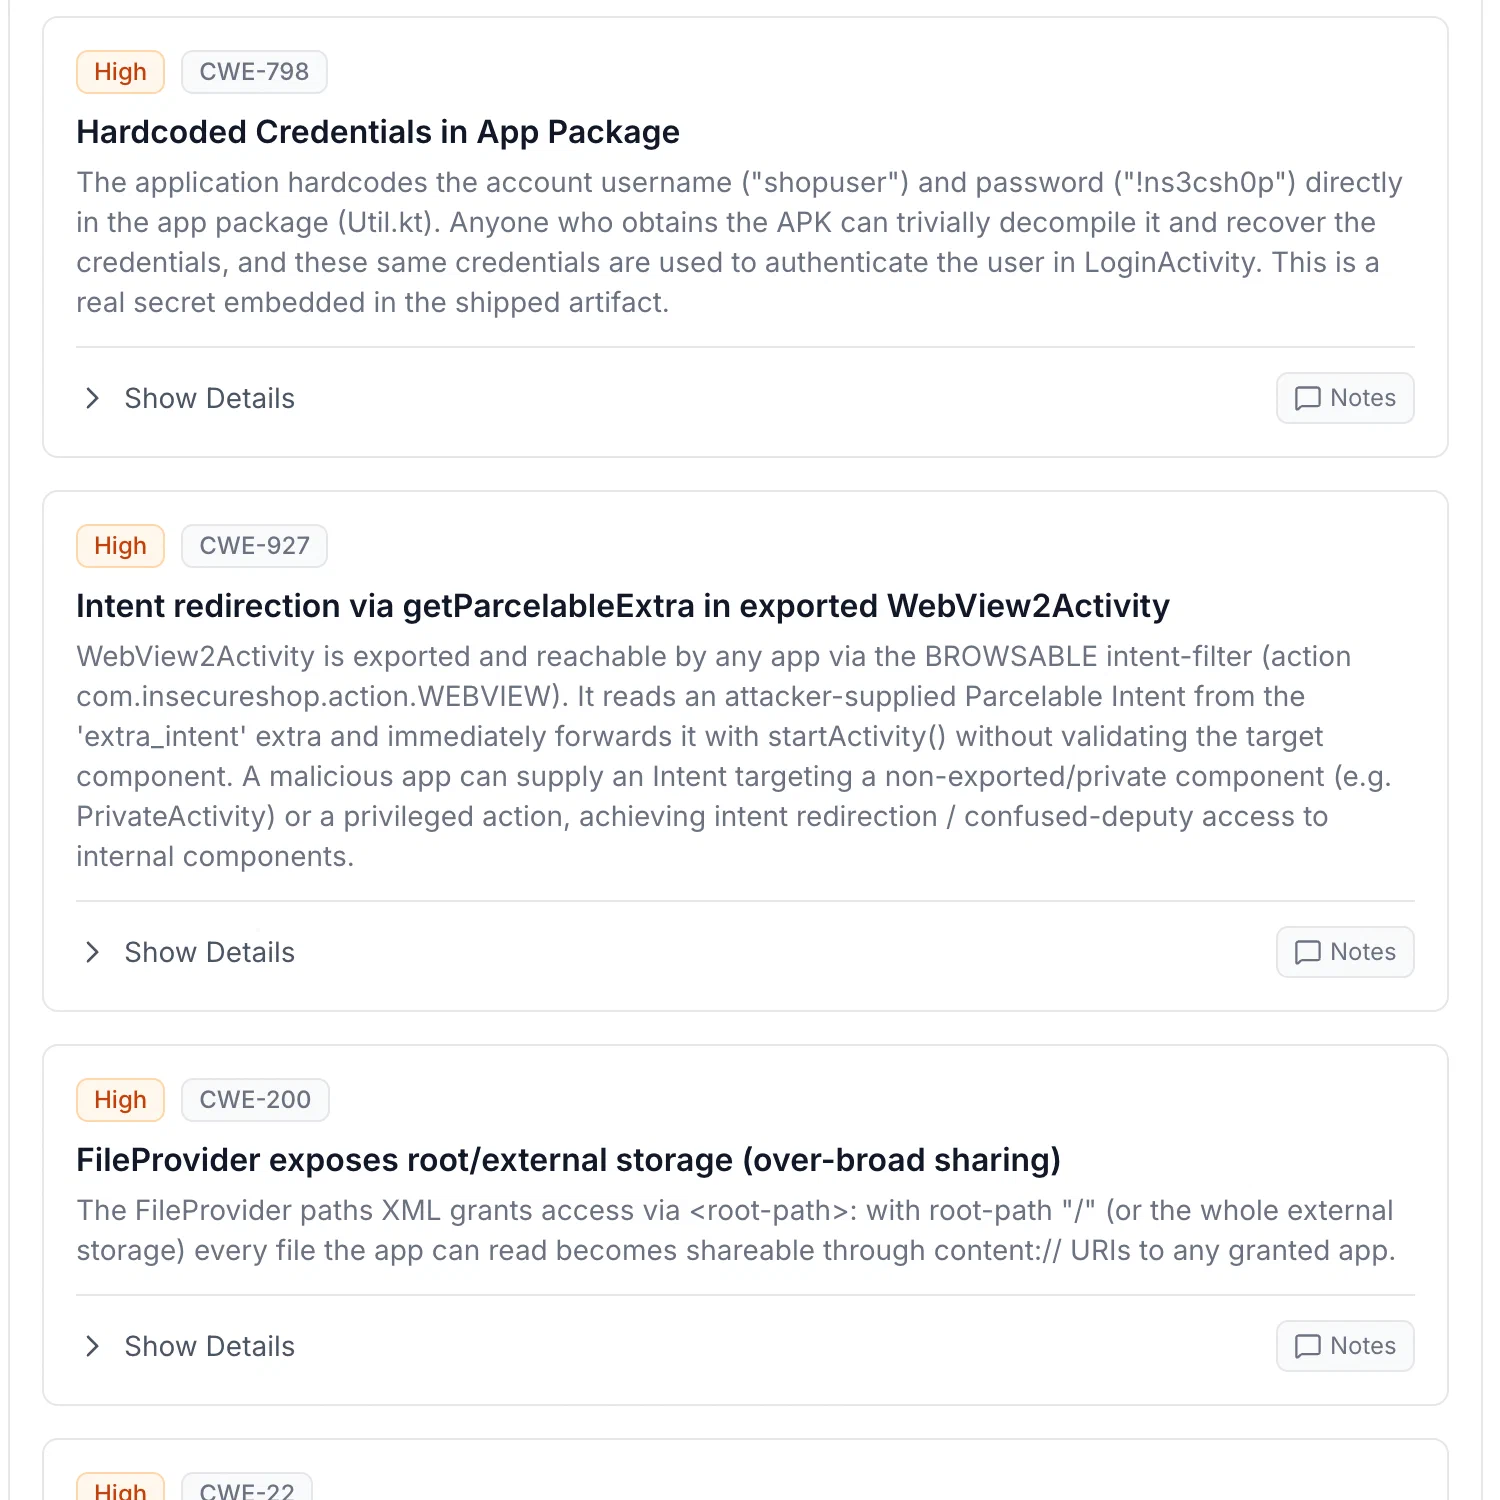
Djini AI SAST findings for the InsecureShop training app, ranked by severity with their CWE mapping

Build your workflow · All Djini use cases →

A few good questions

Before you go deeper.

Does this replace a banking compliance assessment?

These workflows support technical testing and remediation. They do not by themselves constitute a regulatory assessment or certification.

Can we keep testing inside our own environment?

Discuss a private cloud or on-premise enterprise deployment, including the device fleet and model endpoint. A local deployment needs a matching inference and integration design to keep processing local.

Where should a banking team start?

Start with an app release, controlled test accounts, and an agreed journey. Add source scanning in CI/CD and expand the backend scope as part of the evaluation.

DJINI FOR FINTECH & BANKING

Your next release. A sharper security review.

Connect the code, the device, and the question your team needs answered.