
04 / SAAS & ENTERPRISE APPS

SaaS security reviews. Move the whole team forward.

Connect the security review to the teams shipping the product. Use AI SAST inside development, explore AppSec Portal for coordinated release work, and retain research value through the model-improvement roadmap.

  1. 01
    RELEASE REQUESTMobile apps + API + scoped web portal
  2. 02
    APPSEC PORTALPO agent assigns specialist work
  3. 03
    FINDINGSValidation + engineering ownership
  4. 04
    FOLLOW-UPFix workflow + retest status

RELEASE COORDINATION / DEVELOPER WORKFLOWS / MODEL IMPROVEMENTSourceRuntimeEvidence

MOBILE SECURITY USE CASES FOR SAAS

The review needs an owner, and the findings need a next step.

Mobile clients, APIs, and web portals often belong to different engineering teams. Djini’s platform story joins specialist testing with the coordination and follow-up needed to resolve a risk.

01 / Industry use case

Coordinate a review across product teams

A release can involve mobile, backend, and web owners. The security work needs coordinated scope and clear follow-up.

Explore the workflow →

How Djini does the work

In a scoped AppSec Portal deployment, give the PO agent a release-review objective. Route tasks to the configured specialists, validate the findings, and bring remediation into the team’s channels and repository.

The outcome for your team

A release-level review with technical evidence, assigned follow-up, and visibility into the work still required before closure.
02 / Industry use case

Put mobile security review in every PR

Developers need actionable source findings within the tools where they prepare and review a change.

Explore the workflow →

How Djini does the work

Run Djini AI SAST on the mobile source from your pipeline. Feed relevant findings into the coding-agent workflow for a proposed patch, code review, and a new scan.

The outcome for your team

File-level evidence and remediation context connected to a controlled pull-request workflow.

03 / Industry use case

Build a model-improvement programme

An enterprise team can retain useful knowledge from research outcomes and failed model tasks instead of treating each run as isolated.

Explore the workflow →

How Djini does the work

Explore the Finetune Studio roadmap around defined security tasks, validated device outcomes, targeted training data, and held-out evaluation before adopting an updated model.

The outcome for your team

An evaluation plan for the learning loop, including how the team will distinguish a useful model improvement from a regression.

YOUR FIRST EVALUATION

Scope one release with clear engineering ownership.

Choose the mobile app and backend scope first. Run the available testing workflows now, then discuss the Portal agents and integrations needed to coordinate the broader review.

Start with the first workflow →

AppSec Portal is an enterprise scope. AI SAST and CI/CD are available independently.

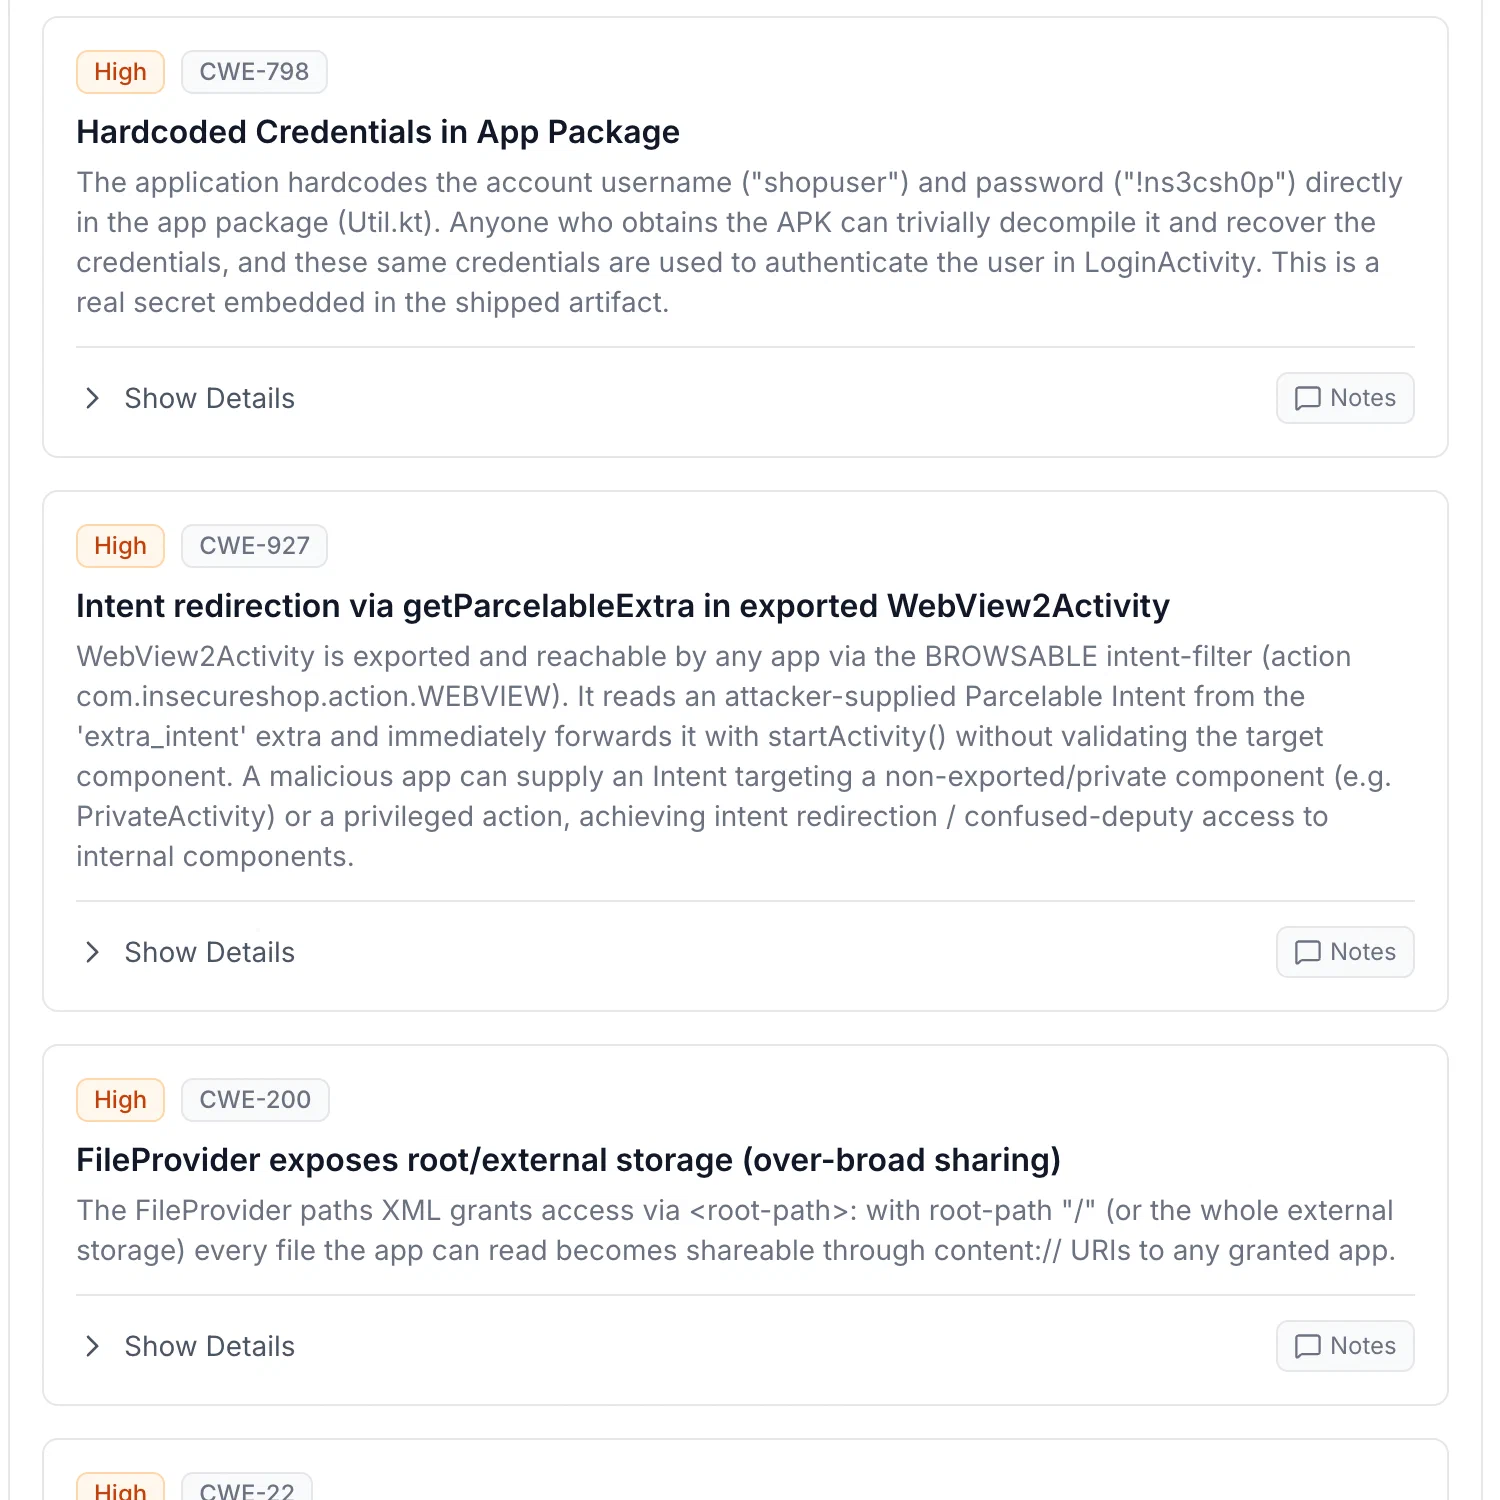
Djini AI SAST findings for the InsecureShop training app, ranked by severity with their CWE mapping

Build your workflow · All Djini use cases →

A few good questions

Before you go deeper.

Is the AppSec Portal included in standard plans?

The coordinated agent organisation is an enterprise workflow. Confirm available roles, channels, integrations, and rollout scope with Djini.

Can we start with source scanning now?

Yes. AI SAST and pipeline access are available independently of the Portal. Start with your mobile repository and an OpenAI-compatible model provider.

Is the self-improving model loop already available?

The supplied roadmap marks automated research loops and the specialised fine-tuned model as upcoming. Finetune Studio is presented as an enterprise roadmap discussion.

DJINI FOR SAAS & ENTERPRISE APPS

Your next release. A sharper security review.

Connect the code, the device, and the question your team needs answered.