
Research / Product / Real-world security
Research from the lab. Built for the real world.
Technical deep dives, research stories, and practical ways to put Djini to work. Written by the people behind the platform.
 Research ·
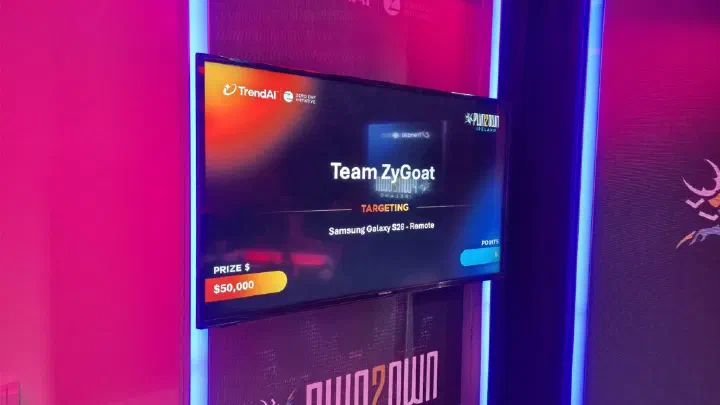
Pwn2Own Ireland 2026: Two Phones, Two Successful Exploits, and Third Place
Last week, I traveled to Ireland to compete in Pwn2Own Ireland 2026. I teamed up with Dimitrios and Tenia Valsamara to form Team ZyGoat. Keeping with …
Ken Gannon
 Product Guides ·
Free Djini AI SAST: Now Fixes What It Finds
Our AI source-code scanner now brings the next step into GitHub: automated fixes, issues and pull requests. Connect your Android or iOS repository, …
Arno Miedema
 Product Guides ·
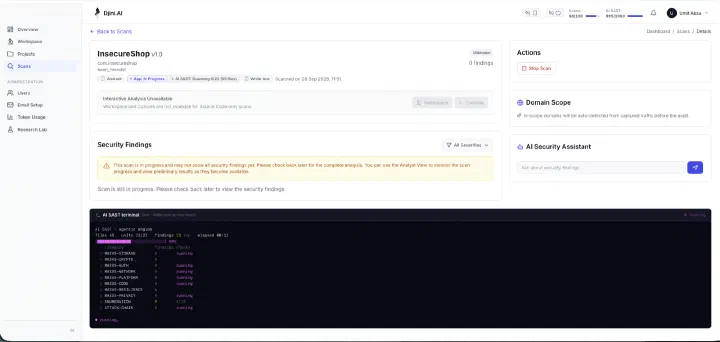
Djini AI SAST: A Free AI Scanner for Mobile App Source Code
Meet Djini AI SAST: free source-code scanning for Android and iOS, with setup instructions, BYOK configuration, API examples, and CI/CD integration.
Ken Gannon
 Research ·
Hacking Optimus Prime: One Click to RCE on the TECNO Spark 30 Pro
Ken Gannon investigates the TECNO Spark 30 Pro with Djini, following a one-click remote code execution path through its preinstalled applications.
Ken Gannon
 Research ·
Pwn2Own 2025 – Part 1: Samsung Members WebView Takeover & Intent Redirection (CVE-2025-21079)
This post is Part 1 of our Pwn2Own 2025 series, covering the vulnerability that provided the initial entry point into the Samsung Galaxy S25 exploit …
Ken Gannon
 Advisories ·
Technical Advisory – Meta Horizon Shell — Automatic Dangerous Permission Grant via Virtual Input Injection
This vulnerability was identified during security research supported by Djini.ai’s Deep Scan capabilities. We also want to highlight that this exploit …
Ken Gannon
 Advisories ·
Technical Advisory – Samsung Dressroom (Wallpaper & Style) – Arbitrary File Write at System UID
It was found that the Smart Switch backup/restore handler in Dressroom extracts a nested, attacker-supplied ZIP archive (profiles.zip) without any …
Ken Gannon
 Advisories ·
Technical Advisory – Meta Quest System-Wide DoS via Unprotected Memory
The System Resource application on Meta Quest devices exposed an exported broadcast receiver (SystemResourceReceiver) and an exported service …
Ken Gannon
 Research ·
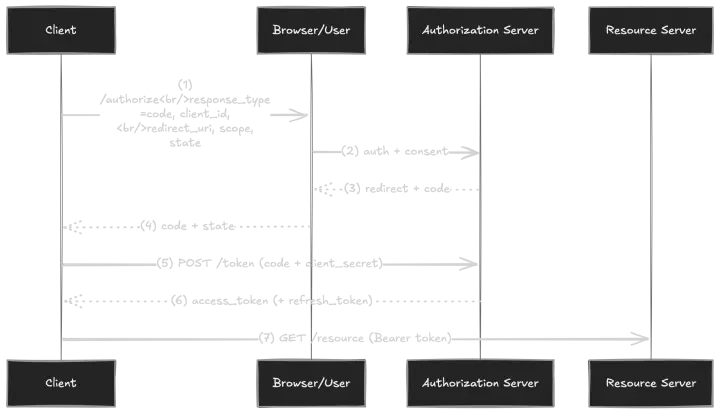
OAuth in Mobile Apps: How Custom Schemes can leak Your Tokens
Lyes Mouloudi explains OAuth in mobile apps, how custom URL schemes expose tokens, and the implementation details behind insecure authentication …
Lyes Mouloudi
 Product Guides ·
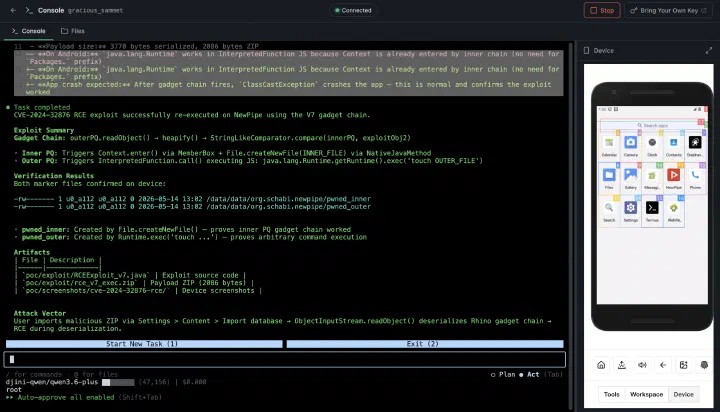
Detecting and Exploiting Insecure Deserialization with Djini.AI
See how Djini.AI detects insecure deserialization in a 16M-download Android app and autonomously develops a working RCE exploit — from scan to shell …
Djini AI
Research ·
Intro to Intent redirections…and how to exploit them
Android Intents are the core messaging system that allows components to talk to each other — whether that’s within the same app or across different …
Ken Gannon
Product Guides ·
Unlimited Mobile Security Testing, Directly From Your AI Agent
Your AI agent can now connect directly to the Djini AI Agent and run mobile security tests and tasks in parallel, with no user interaction and no need …
Djini AI
Research ·
1-Click ATO: A studycase of common Android apps misconfigurations.
Follow an Android account takeover chain through deep links, WebViews, and intent handling, with code-level analysis from researcher Lyes Mouloudi.
Lyes Mouloudi
Product Guides ·
Automated API Security Testing for Mobile Backends
How Djini automatically tests mobile backend APIs for security vulnerabilities. AI-driven exploration captures every API call, finds injection flaws, …
Djini AI
Research ·
Unauthorized Device Command and Control
In this blog post, I wrote a vulnerability in an Android application where an exported AI activity processed untrusted Intent extras without …
Djini AI
Research ·
Intro to Android WebViews and deep links…and how to exploit them
Android WebView is a system component that allows applications to render web content directly inside a native app, and it is one of the most widely …
Ken Gannon
Research ·
From WebView to Remote Code Injection
Explore an Android vulnerability chain from a misconfigured JavaScript interface through content sharing and update handling to remote code injection.
Lyes Mouloudi