09 / INDIVIDUAL RESEARCHERS & BUG BOUNTY HUNTERS

Your curiosity. A whole research lab.

Put Djini to work on your next mobile investigation. Explore Android and iOS apps, validate findings on devices, and build your expertise with Mobile Hacking Lab Academy training.

DJINI AI + DEVICE LAB
  1. 01
    YOUR TARGETApp build + research scope
  2. 02
    DJINI ANALYSISCode paths + runtime behavior
  3. 03
    DEVICE LABBuild PoC → run → inspect
  4. 04
    YOUR FINDINGReproduction + impact evidence

RESEARCHERS & BUG BOUNTYMobile bug bountyDevice-tested PoCsTraining included

You ask Djini

“Investigate this mobile app, follow the most promising attack path, and build a PoC I can run on the device to demonstrate the impact.”

What your team gets

An investigation connecting the code path, tested behavior, PoC, and evidence you can review for a bounty report or disclosure.

Access & scope

AppSec for mobile application testing; Research for advanced native analysis, fuzzing, and PoC workflows. Both include Mobile Hacking Lab training.

THE WORK BEHIND THE OUTCOME

Spend more time on the finding that matters.

Independent research means connecting many small jobs: understanding an app, following a promising path, preparing a test, and collecting evidence. Give Djini that connected workflow while you direct the investigation.

  1. 01

    Choose your research target

    Bring an Android or iOS app, the relevant build, and the research scope. Work from a binary, or add source code when it is available.

  2. 02

    Follow the interesting behavior

    Use analysis, agentic chat, and runtime investigation to explore app logic, component interactions, and connected APIs. Pursue the paths that matter to your hypothesis.

  3. 03

    Build and run the proof

    Have Djini prepare a PoC and test it on the selected device. Inspect the result, refine the experiment, and establish the conditions needed to reproduce it.

  4. 04

    Prepare the evidence

    Bring together the affected version, reproduction steps, PoC, and observed impact. Review the findings and shape them into your bug bounty submission or disclosure.

INSIDE DJINI

Your agent. Your device. Your investigation.

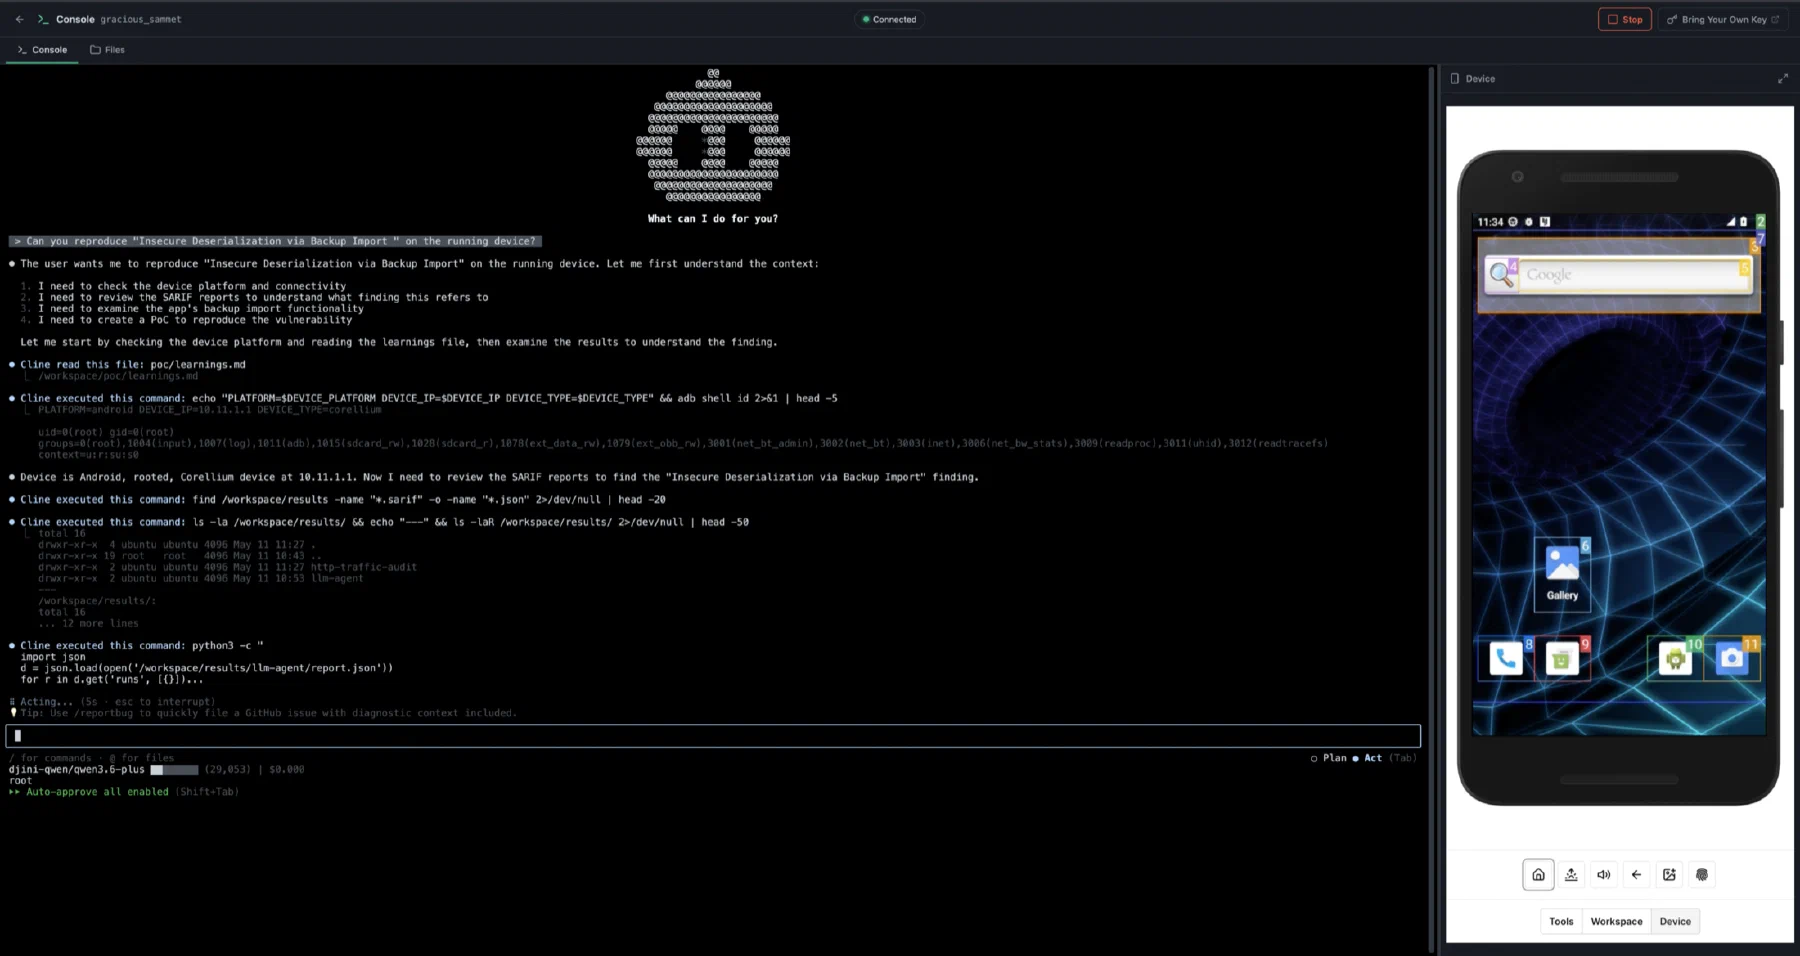
Move from the research conversation to the terminal and connected device in the same workspace. Follow what Djini is doing and use the results to decide where to investigate next.

The Djini agentic console reproducing a finding on a connected Android test device

The Research bundle

Follow the coverage. Build the proof.

Take the investigation into native code. Connect analysis, coverage-guided fuzzing, and autonomous PoC building and testing in one workspace.

01 / Coverage-guided fuzzing

Make each experiment more informed.

Have Djini help build a focused fuzzing harness for a native library or parser. Use execution coverage to explore new paths, evolve the input corpus, and identify crashes worth investigating.

  • Harness
  • Coverage feedback
  • Crash triage

02 / Autonomous PoC building & testing

Put the hypothesis on a device.

Let Djini build and run a proof of concept, inspect the execution result, and refine the test. Bring the generated code, device traces, and reproduction conditions back into your investigation.

  • Build
  • Run on device
  • Inspect & refine

You choose the target and assess the evidence. A reproduced crash, a confirmed vulnerability, and a working exploit are distinct research outcomes.

WHAT YOU TAKE AWAY

A finding you can demonstrate

Connect the claim to a device result, target version, and reproducible test.

Research artifacts you can inspect

Review the generated PoC, traces, and execution output as part of your investigation.

Skills that compound

Put your included Academy course to work on the same testing and research tasks you are pursuing with Djini.

Built by researchers. Proven in the arena.

Pwn2Own Ireland · October 2026

The people behind Djini break boundaries.

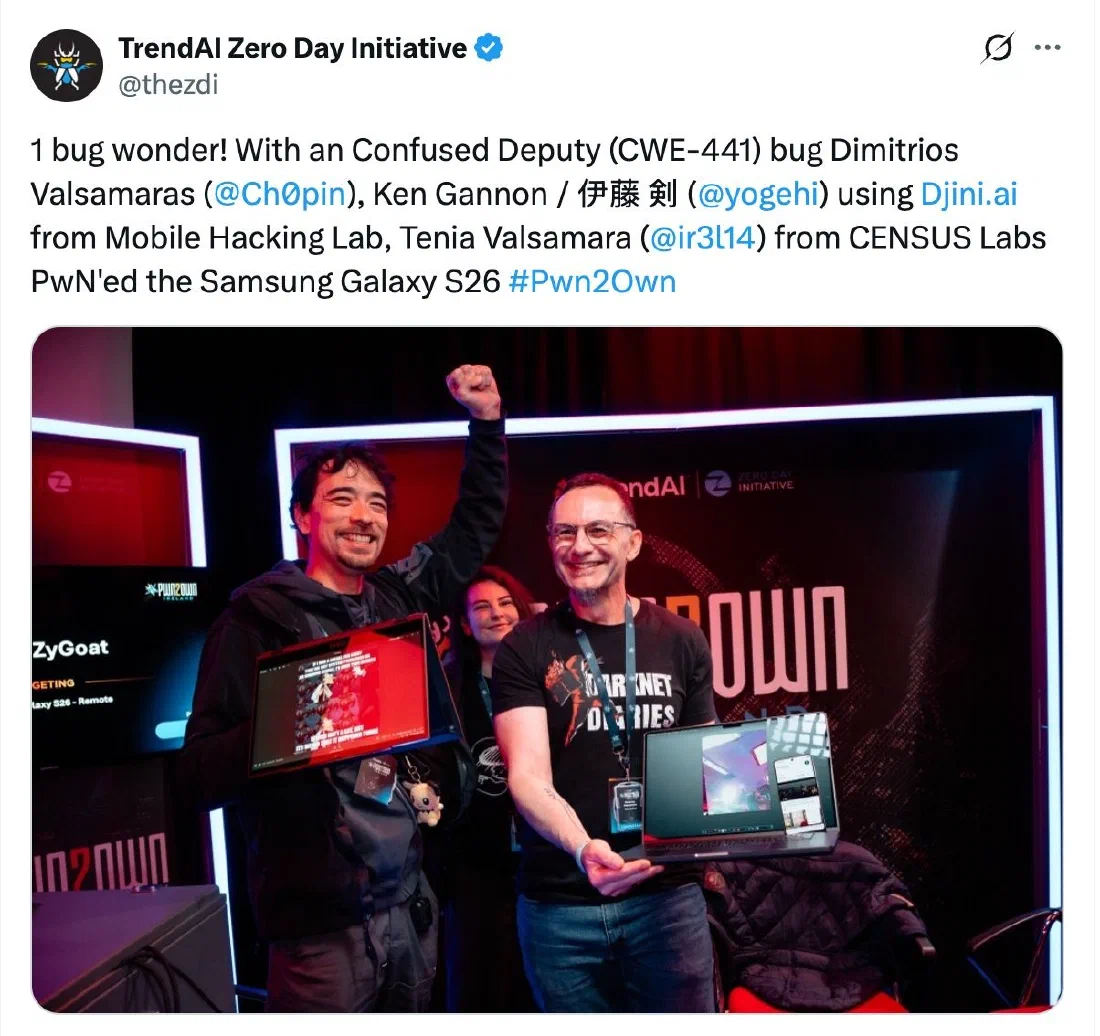
At Pwn2Own Ireland 2026, researchers used Djini.ai in successful demonstrations against two flagship phones. ZDI named Djini in the official results.

Research by Dimitrios Valsamaras, Ken Gannon of Mobile Hacking Lab, and Tenia Valsamara of CENSUS Labs. Photo and result reporting: TrendAI Zero Day Initiative. Awards recognise the researchers' demonstrated results.

TrendAI Zero Day Initiative's post crediting Dimitrios Valsamaras, Ken Gannon using Djini.ai, and Tenia Valsamara for exploiting the Samsung Galaxy S26 at Pwn2Own
Djini.ai, in ZDI's own words.

More research with Djini · All research & advisories →

Start curious. Go deeper.

Your next finding starts for free.

From your first scan to an enterprise security program. Choose how far you want to go.

Meet Djini

Free

€0 / month

Put your first app to the test.

  • 10 AI SAST scans per month
  • 1 blackbox AI SAST + dynamic scan (welcome credit)
  • Bring your own model key
  • No credit card required

Build securely

AppSec

€150 / month
€1,440 €1,800 / year

Everyday mobile security testing.

  • 10 monthly app scans
  • Android & iOS AppSec
  • AI agentic chats
  • €100 AI budget / month
  • MHL Academy AppSec training
  • CAPT & CIPT certification exams
  • Yearly AppSec also includes Advanced Android Hacking + the CAAH exam

Your perimeter

Enterprise

Built around your team

Your infrastructure. Your control.

  • Private & on-premises deployment
  • CI/CD integration
  • Team & user management
  • Custom private AI models
  • Full MHL Academy access

AI SAST requires BYOK; model usage is billed separately by your provider. The blackbox welcome scan is a one-time new-account credit. Device Lab capacity and usage depend on your plan.

A few good questions

Before you go deeper.

Which bundle should I choose?

Choose AppSec for Android and iOS app testing, mobile bug bounty work, and the CAPT/CIPT certification path. Choose Research for native-code investigation, coverage-guided fuzzing, autonomous PoC building and testing, and an included Android or iOS Userland Fuzzing & Exploitation course.

What do I get with yearly billing?

Both bundles save 20% compared with twelve monthly payments: AppSec is €1,440 per year and Research is €2,400 per year. Yearly AppSec also includes Advanced Android Hacking and the CAAH certification exam. Research includes your choice of the Android or iOS userland course.

Will Djini submit reports or guarantee a bounty?

You review the evidence and submit the report to the programme. A bounty depends on the programme’s scope, impact assessment, and duplicate policy. Djini helps with investigation and reproduction; it does not guarantee an accepted submission or reward.

PUT DJINI TO WORK

Your next target. Your next breakthrough.

Start with 10 free AI SAST scans each month. Choose a bundle when you are ready to go further.